A new location should create revenue and capacity, not a new set of technology problems. Yet many growing businesses open a branch, warehouse, clinic, or office with internet installed at the last minute, equipment selected independently, and no clear plan for security or support. This multi site network rollout case study illustrates how a disciplined rollout approach can protect uptime while giving every site a consistent technology foundation.
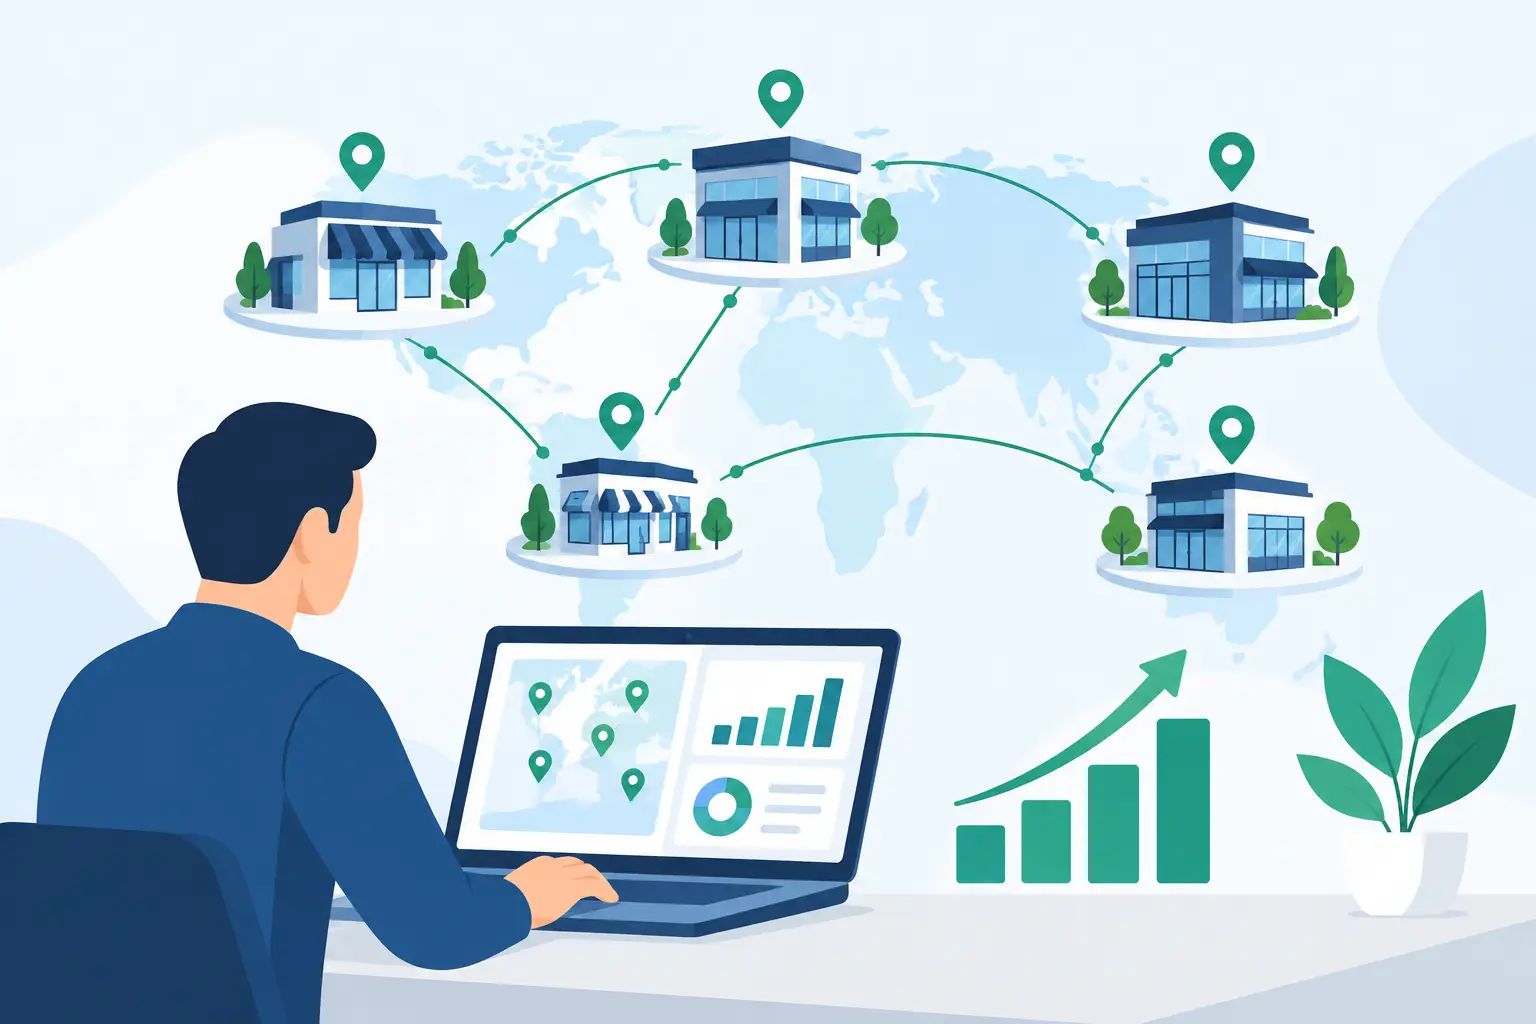
The organization in this example is representative of a growing Midwest business with a headquarters and six distributed locations. Its leadership needed each location to access shared applications, communicate reliably, process transactions, and protect customer and company data. Just as importantly, they needed one accountable technology partner instead of separate internet providers, hardware vendors, security contractors, and support contacts.
The business problem was consistency, not just connectivity
The organization had expanded over several years, and each site had evolved differently. Some locations used aging switches and consumer-grade wireless equipment. Others had newer equipment but inconsistent configuration standards. Internet circuits varied widely, and a few locations depended on a single connection with no practical backup plan.
That inconsistency had a real operational cost. Staff experienced unreliable Wi-Fi, video calls dropped during customer conversations, and troubleshooting often required someone to determine which vendor owned which part of the problem. Headquarters had limited visibility into site performance, making it difficult to spot an issue before it affected operations.
Security was also a concern. Guest wireless traffic was not consistently separated from business devices. Network equipment did not follow a uniform patching or firmware process. As the company prepared to add more locations, leadership recognized that repeating the existing model would multiply risk and support costs.
The goal was not simply to replace hardware. The company needed a network model that could be deployed repeatedly, managed centrally, and adapted to the different realities of each location.
Multi site network rollout case study: defining the standard
Before ordering equipment, the project team completed a site-by-site discovery process. This step established what each location actually required rather than assuming every site should receive the same configuration.
The assessment reviewed floor plans, available cabling, user counts, wireless coverage needs, existing internet service, critical applications, phones, cameras, printers, and any specialized equipment. A small office with 15 employees did not need the same switching capacity as a warehouse with scanners, cameras, and a larger number of connected devices. Standardization mattered, but so did right-sizing.
From that review, the team developed a repeatable network blueprint. Each site would receive a business-class firewall, managed switches, centrally managed wireless access points, segmented network access, and documented internet failover options. The design separated core business systems from guest Wi-Fi, voice traffic, physical security devices, and other connected equipment that did not need access to sensitive resources.
This segmentation reduced the blast radius of an issue. If a guest device or camera network encountered a problem, it would not automatically have a path to critical applications. It also improved performance by allowing traffic policies to prioritize services such as voice, cloud applications, and point-of-sale activity where needed.
The blueprint was intentionally flexible. Locations with limited broadband availability received a different failover design than sites in well-served commercial areas. A site that relied heavily on cloud software had different bandwidth targets than one using mainly local systems. The standard was not a rigid equipment list. It was a defined operating model for performance, security, and support.
Planning around business operations
Network projects fail when technical decisions are made without considering how the business operates. For this rollout, site cutovers were scheduled around each location’s busiest hours, staffing levels, and critical processes. A location that processed shipments early in the morning required a different maintenance window than an office that conducted client meetings throughout the day.
The project plan also identified dependencies early. New circuits can take longer than expected, especially when construction, landlord approvals, or provider scheduling are involved. Structured cabling needs, electrical availability, equipment mounting, and physical security integrations were reviewed before deployment dates were committed.
Each site received a documented runbook covering the installation sequence, device naming standards, network segments, escalation contacts, and validation requirements. This may sound administrative, but it prevents the most common cause of multi-site rollout delays: decisions being made on-site without the right people, information, or approvals available.
Stakeholder communication was equally important. Site managers knew what to expect, when any interruption could occur, and how to report issues after go-live. Employees received practical instructions for joining the new wireless network and connecting approved devices. Clear communication reduced uncertainty and kept local teams from creating workarounds that could weaken security.
Deployment used a repeatable, low-disruption process
Equipment was preconfigured before it arrived at each site. Firewalls, switches, and access points were labeled, loaded with approved configurations, and tied to the central management environment. That allowed technicians to focus on physical installation, connectivity testing, and local adjustments rather than building each network from scratch in a live business environment.
At each location, the deployment followed a controlled sequence: confirm the internet circuit, install and connect edge equipment, bring up wired and wireless services, apply segmentation policies, and validate access to business systems. Technicians then tested voice quality, application performance, guest isolation, remote access requirements, and failover behavior.
Testing failover was particularly important. A backup connection has little value if no one confirms that it activates correctly and that essential traffic can continue across it. The team simulated a primary circuit interruption and verified that critical services remained available. Expectations were set appropriately: failover may preserve business continuity, but its bandwidth may not equal the primary connection. The organization prioritized critical applications during a failover event instead of expecting every nonessential service to perform normally.
The rollout was phased rather than completed simultaneously across every site. The first location served as a controlled deployment to validate the design and refine the installation process. Lessons from that site improved the schedule, documentation, and onsite workflow for the remaining locations. This added a small amount of time at the beginning but avoided repeating preventable problems six times.
Results: better visibility and a stronger operating model
Once the rollout was complete, the organization had a consistent network environment across all sites. IT leadership could view device status, connection health, and wireless performance from a central management platform rather than relying on calls from individual offices to identify a problem.
Support also became more efficient. Standardized equipment and configurations meant that technicians could diagnose issues faster, maintain a clearer inventory, and apply updates through a more controlled process. Instead of asking what had been installed at a particular branch years earlier, the support team worked from current documentation and a known design.
The security improvement was just as meaningful. Segmented networks reduced unnecessary access between users, guest devices, cameras, and business systems. Central policy management made it easier to maintain consistent protections as locations changed. The company was also better positioned to demonstrate reasonable network controls to customers, insurers, and compliance stakeholders.
There were trade-offs. Higher-quality connectivity, managed equipment, and redundant options require investment. Not every site justified identical redundancy or bandwidth. The value came from matching each location’s design to the cost of downtime, its operational requirements, and the sensitivity of the data it handled.
What growing organizations should take from this case study
A multi-site network is not a collection of separate offices with internet access. It is one operating environment that supports employees, customers, applications, communications, and security controls across the business.
The most effective rollouts start with a clear standard, but they do not ignore local conditions. They document the environment before making changes, preconfigure equipment where possible, test both normal operation and failure scenarios, and keep site leaders informed throughout the process. They also account for what happens after installation, including monitoring, patching, support ownership, and future expansion.
For organizations opening locations, consolidating technology, or replacing an inconsistent network, the right partner should be able to manage connectivity, infrastructure, cybersecurity, voice, and physical technology as connected parts of the same business system. Plasma Networks approaches projects with that full operational view, helping clients build networks that are ready for the next location rather than merely functional on opening day.
A well-planned rollout does more than get a new site online. It gives leadership confidence that each location can perform, recover, and grow without turning technology into the next operational bottleneck.